Turning AI Agent Slop Into Gold: A Practical Guide to Agent Trust
AI coding agents have changed the economics of writing software. A developer can now ask an agent to implement a feature, fix a bug, add tests, and open a pull request in a fraction of the time it once took to do the work manually. That is useful—but it also means more code arrives, more quickly, and from contributors that may not understand the whole system.
The hard problem is no longer simply how to generate code. It is how to increase delivery speed without lowering the quality bar. An agent that produces ten times as many changes is not a productivity win if those changes create ten times as many regressions.
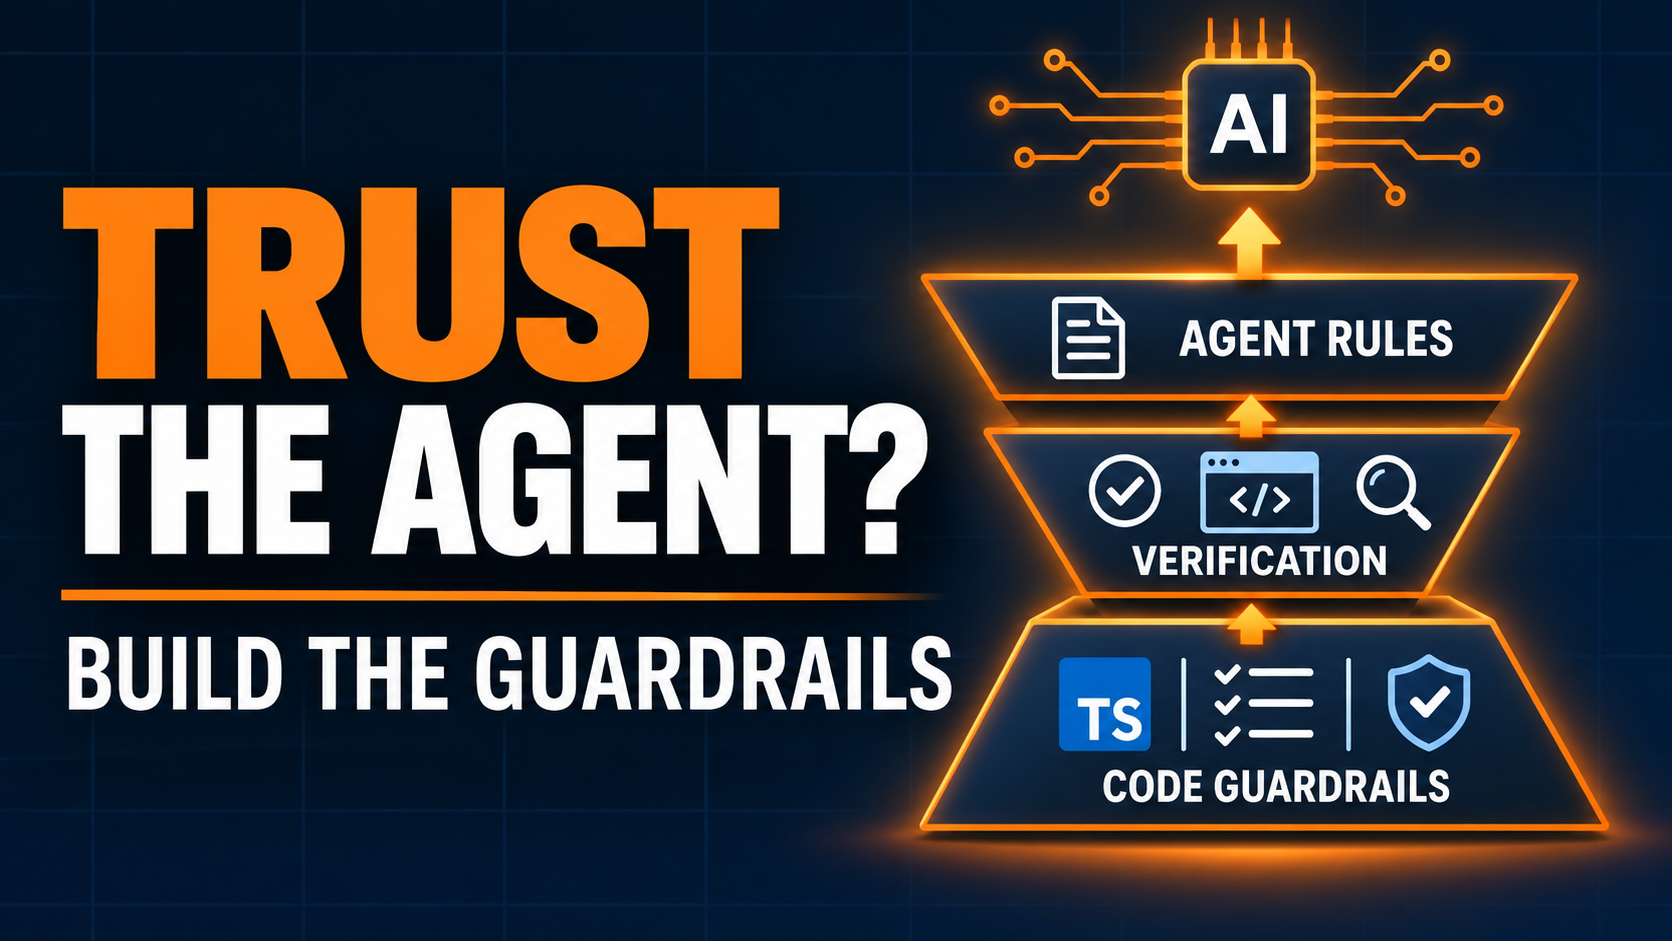
In her talk about building a high-trust agent environment, Lauren Tan (known as Potato) described this as an investment in trust rather than blind faith. She described an inverse pyramid: deterministic constraints in the codebase at the bottom, verification in the middle, and written instructions for agents at the top. The team-specific results she reported included 11,000 pull requests shipped in a month and a revert rate of about 0.5%. Those are results from her team’s environment, not a promise that a particular tool or configuration will produce the same outcome for every project.
This guide turns that idea into a practical implementation plan for a TypeScript codebase. The examples use common tools—TypeScript, ESLint, dependency-cruiser, Vitest, fast-check, and Playwright—but the principles apply whether you build a Node.js API, a React application, or a full-stack product.
The trust model: make the right path the easiest path
Think of the agent environment as three layers. The bottom layer is deterministic constraints: compiler checks, API design, lint rules, and dependency boundaries. These checks give the agent less room to invent its own conventions. The middle layer is verification: unit tests, integration tests, browser-driven tests, fuzzing, and—where justified—formal methods. The top layer is prose: AGENTS.md, project instructions, reusable skills, and task-specific acceptance criteria.
The order matters. If a review comment says “do not import database code into the browser,” a markdown instruction can remind an agent, but a dependency rule can reject the import every time. If an agent repeatedly forgets to await a promise, a typed lint rule can catch it before the change is merged. A rule enforced by the tools is more repeatable than a rule that depends on the model remembering a paragraph.
A useful rule of thumb: when you correct the same agent mistake more than once, ask whether you can turn the correction into a compiler error, lint error, architectural boundary, or test.
1. Strengthen the TypeScript foundation
Start with the compiler. TypeScript is not a substitute for tests, but strict type checking prevents a meaningful class of mistakes from reaching runtime. The TypeScript compiler options reference documents the available checks. For a new project, or a project that already has reasonable type hygiene, consider these options:
{
  "compilerOptions": {
    "strict": true,
    "noUncheckedIndexedAccess": true,
    "exactOptionalPropertyTypes": true,
    "noImplicitOverride": true,
    "noFallthroughCasesInSwitch": true
  }
}
strict enables the strict family of checks, including null checking and implicit-any checking. noUncheckedIndexedAccess adds undefined to indexed lookups, which forces code to account for a missing array element or dictionary key. exactOptionalPropertyTypes makes the difference between an omitted property and a property explicitly set to undefined visible in the type system. noImplicitOverride makes subclass overrides explicit.
Do not switch every flag on in a legacy repository and then let an agent “fix all the errors” in one enormous change. Enable the checks in a branch, assess the error volume, and migrate by package or directory. Keep the module and module-resolution settings appropriate for your runtime or bundler; the example above only shows the type-safety settings.
TypeScript types stop at the runtime boundary
One important limitation is easy to miss: TypeScript types are erased at runtime. An HTTP request, database row, message queue payload, local-storage value, or third-party API response is not made trustworthy just because you assign it a TypeScript interface. Validate untrusted data before treating it as a domain type.
For example, use a runtime schema library such as Zod to parse an incoming request. Add it to an existing project with npm install zod. The important pattern is that application code receives the parsed value—not the original untrusted object:
import { z } from "zod";

const createTeamSchema = z.object({
  name: z.string().trim().min(1),
  visibility: z.enum(["private", "public"])
});

type CreateTeamInput = z.infer<typeof createTeamSchema>;

const parsed = createTeamSchema.safeParse(req.body);

if (!parsed.success) {
  return res.status(400).json({ error: "Invalid request" });
}

// parsed.data is validated and has the inferred TypeScript type.
await teamService.create(parsed.data);
Use this pattern at system boundaries, not around every internal function call. Define the schema once, infer the TypeScript type from it, and make parsing part of the route, message-consumer, or adapter. That prevents the agent from inventing a type assertion such as req.body as CreateTeamInput and accidentally bypassing the actual validation.
2. Turn repeated code-review corrections into ESLint errors
A lint rule is most useful when it encodes a concrete engineering decision. Do not begin by banning syntax because it looks unfashionable. Look at recent pull requests and identify the patterns that repeatedly cause bugs, performance problems, or review debates. Then add a rule with a message that explains the approved alternative.
For TypeScript projects, typescript-eslint provides TypeScript-aware rules. Its type-checked configurations can catch issues that basic syntax linting cannot, although they take longer because TypeScript must provide type information. The official typed-linting guide shows the flat-config setup.
Install the core packages:
npm install --save-dev eslint @eslint/js typescript typescript-eslintA starting flat configuration can look like this. It enables the recommended rules and type-aware rules for TypeScript files:
// eslint.config.mjs
import js from "@eslint/js";
import { defineConfig } from "eslint/config";
import tseslint from "typescript-eslint";

export default defineConfig({
  files: ["**/*.{ts,tsx}"],
  extends: [
    js.configs.recommended,
    tseslint.configs.recommended,
    tseslint.configs.recommendedTypeChecked
  ],
  languageOptions: {
    parserOptions: {
      projectService: true
    }
  },
  rules: {
    "@typescript-eslint/no-floating-promises": "error",
    "@typescript-eslint/no-unsafe-assignment": "error"
  }
});
Two useful examples are no-floating-promises, which catches promise-like expressions that are not properly handled, and no-unsafe-assignment, which prevents values typed as any from silently flowing into more specific variables. These are especially valuable in agent-written asynchronous code and at poorly typed library boundaries.
You can also prohibit a library or import path that your project has deliberately replaced. ESLint’s no-restricted-imports supports custom messages and path patterns:
// Add inside the rules object in eslint.config.mjs:
"no-restricted-imports": [
  "error",
  {
    paths: [
      {
        name: "moment",
        message: "Use the shared date utilities from @/shared/date."
      }
    ]
  }
]
You can scope rules to particular files. For example, add an override for src/client and src/components that rejects imports from @/server/**, while leaving server-side code free to import server modules. ESLint is good at enforcing direct import restrictions. For rules about the whole dependency graph—including transitive relationships—add a dependency-graph tool in the next step.
Be deliberate when banning an API
The talk gives a striking example: the team banned React’s useEffect from most product code because it was repeatedly misused in that application. The broader lesson is not that every TypeScript or React project should ban useEffect. It is that an API requiring subtle knowledge may be a poor default for your codebase. You might replace a broad API with a simpler project-specific hook or service, then enforce the preferred entry point.
The same idea applies to timers. If developers repeatedly use setTimeout or requestAnimationFrame to patch around a state-management problem, consider a scheduler or state-driven API that owns the timing behavior. ESLint’s no-restricted-syntax and no-restricted-globals can enforce carefully chosen restrictions. Keep legitimate exceptions explicit and narrow—for example, allow the timer only inside the scheduler implementation.
Do not blindly ban comments. Comments that merely repeat what the code says become noise, and comments are not enforcement. But comments that explain a non-obvious invariant, a security decision, or why an exception exists can be valuable. The goal is to replace “please don’t do this” comments with executable constraints, not to remove useful design context.
3. Enforce architecture with dependency boundaries
Folder names communicate architecture to people and agents, but they do not enforce it. A client module can still import a server module, a domain module can still depend on a database adapter, and two unrelated features can still become tangled through circular imports.
Choose a small number of boundaries that matter to your application. A typical full-stack TypeScript project might start with:
src/
  client/       # browser-only code and UI
  server/       # routes, database adapters, secrets
  domain/       # business rules and domain types
  shared/       # code genuinely safe on both sides
The exact names are unimportant. The direction of dependencies is what matters. For example, browser code may depend on shared contracts, but it must never reach into server implementation code. Domain logic should not import Express, React, or a database client.
dependency-cruiser validates module relationships and supports forbidden rules. Install it with npm install --save-dev dependency-cruiser. A minimal configuration might look like this:
// .dependency-cruiser.cjs
module.exports = {
  forbidden: [
    {
      name: "client-must-not-import-server",
      severity: "error",
      from: { path: "^src/(client|components)/" },
      to: { path: "^src/server/" }
    },
    {
      name: "no-circular-dependencies",
      severity: "error",
      from: { pathNot: "^node_modules" },
      to: { circular: true }
    }
  ]
};
Adjust the regular expressions to match your real folder structure. Run the tool against your source tree and review the findings before making the rule a required CI check. The dependency-cruiser rules tutorial explains how from and to patterns work, how to set severity to error, and how to detect more complex dependency relationships.
Add a script so the check is easy for both developers and agents to run:
{
  "scripts": {
    "check:deps": "depcruise --validate .dependency-cruiser.cjs src"
  }
}
This is more than code organization. In a full-stack app, a boundary between client and server helps reduce the chance that server-only modules, database code, or secret-bearing configuration are pulled into a browser bundle. It is not a complete security boundary by itself—review bundler configuration and runtime exposure too—but it makes one class of architectural mistake visible and repeatable.
You can also use Knip to identify unused files, exports, and dependencies. Removing dead code and outdated packages improves the examples agents see and reduces the number of competing patterns they may copy.
4. Build a verification system that gives agents feedback
Static checks constrain what can be written. Verification checks whether the result behaves as intended. The goal is not to accumulate the highest possible test count; it is to translate product requirements into properties that can be checked automatically.
Start with unit and integration tests
Use the test runner that fits your project. Vitest works well in many TypeScript and Vite-based projects and can also run in projects that do not use Vite. Install Vitest and fast-check with npm install --save-dev vitest fast-check. Cover important business rules, error handling, authorization decisions, data transformations, and integration points. A test should describe an invariant or an observable behavior—not simply mirror the implementation line by line.
For example, a discount calculation should never produce a negative amount, should never increase the original price, and should return integer cents. Those rules are more durable than a test that only checks one hand-picked input.
// money.ts
export function discountedCents(
  priceCents: number,
  discountBasisPoints: number
): number {
  return Math.round(
    priceCents * (10_000 - discountBasisPoints) / 10_000
  );
}
Add generated inputs with fast-check. It works with Vitest and other test runners. Instead of choosing a few examples yourself, fast-check generates many inputs and can shrink a failing case to a smaller reproduction:
// money.property.test.ts
import { describe, expect, it } from "vitest";
import fc from "fast-check";
import { discountedCents } from "./money";

describe("discountedCents properties", () => {
  it("never returns a negative amount or increases the price", () => {
    fc.assert(
      fc.property(
        fc.integer({ min: 0, max: 10_000_000 }),
        fc.integer({ min: 0, max: 10_000 }),
        (priceCents, discountBasisPoints) => {
          const result = discountedCents(
            priceCents,
            discountBasisPoints
          );

          expect(Number.isSafeInteger(result)).toBe(true);
          expect(result).toBeGreaterThanOrEqual(0);
          expect(result).toBeLessThanOrEqual(priceCents);
        }
      ),
      { numRuns: 1_000 }
    );
  });
});
This is a small example, but the technique becomes powerful when you test domain invariants: a user without membership must never read a private project; retrying an idempotent operation must not create a second payment; normalizing a value twice must have the same result as normalizing it once; and a pagination operation must not return duplicate records across adjacent pages. Make the property reflect a business rule that matters.
Test the running application, not just isolated functions
For a web application, give the agent a way to launch the app and exercise real user flows. Playwright provides browser-driven tests with assertions that automatically retry while the browser reaches the expected state. This avoids many timing problems caused by checking a page too early. In an existing project, install it with npm install --save-dev @playwright/test, then download the browser binaries with npx playwright install. You can also scaffold the configuration and example tests with npm init playwright@latest.
import { test, expect } from "@playwright/test";

test("a customer can complete checkout", async ({ page }) => {
  await page.goto("/checkout");

  await page.getByLabel("Email").fill("buyer@example.com");
  await page.getByRole("button", { name: "Place order" }).click();

  await expect(page.getByRole("status"))
    .toHaveText("Order confirmed");
  await expect(page).toHaveURL(/\/confirmation/);
});
Configure Playwright to retain useful diagnostics when a test fails:
// playwright.config.ts
import { defineConfig } from "@playwright/test";

export default defineConfig({
  use: {
    trace: "retain-on-failure",
    screenshot: "only-on-failure",
    video: "retain-on-failure"
  }
});
A Playwright trace can show the actions a test performed, DOM snapshots before and after actions, screenshots, and related logs. That makes the trace a review artifact: instead of asking an agent to say “I tested it,” ask it to attach the failing or passing test output and, for a user-visible change, a trace or screenshot that demonstrates the behavior. See the Playwright Trace Viewer documentation.
Explore UI states with property-based testing
Example-based browser tests only visit the scenarios someone thought to write down. The talk also mentioned Bombadil, an evolving tool for property-based testing of web and terminal UIs. Rather than scripting only fixed click sequences, you define properties that should remain true while the tool generates actions and explores the running interface. For example: the cart total is never negative, a submitted order cannot be submitted twice, and a loading indicator eventually disappears after a request completes.
See the Bombadil manual for its TypeScript specifications and UI exploration model. It is an additional layer, not a replacement for focused Playwright tests. Because the project describes itself as new and experimental, evaluate its reliability and platform support in your own application before making it a blocking production gate.
Give agents a feature map
A feature map is a user-oriented index of the application. It gives the agent a stable vocabulary and tells it where to verify a change. Keep it in the repository, for example at docs/agent-feature-map.md:
# Feature map

## Checkout
- Route: /checkout
- Main flow: cart -> address -> payment -> confirmation
- Key states: empty, submitting, declined, confirmed
- Browser tests: tests/e2e/checkout.spec.ts
- Invariants:
  - A confirmed order has one order ID.
  - A declined payment does not empty the cart.
  - Repeated submission does not create a second order.

## Account settings
- Route: /settings/account
- Main flow: view -> edit -> save -> confirmation
- Browser tests: tests/e2e/account-settings.spec.ts
When you ask an agent to change checkout, you can now refer to the checkout flow and its named states instead of describing “the thing on the page.” You can go further by providing a small, documented CLI that starts the app, seeds test data, opens a browser session, or runs a named flow. A reusable driver is easier to test and reuse than asking every agent to improvise browser setup.
Use formal methods for the small number of flows that justify them
Some bugs are caused by combinations of events rather than a single function: two devices update the same notification, a payment callback races with a retry, or two workers attempt to claim the same job. For these cases, ordinary example tests may not cover enough possible interleavings.
TLA+ and the TLC model checker let you describe system state, allowed transitions, and invariants, then explore the reachable states of a finite model. Model a small version of the workflow first: define the states, define what actions can happen, and state what must always remain true. For a payment flow, an invariant might be “one idempotency key can produce at most one successful charge.”
Be precise about what this proves. TLC checks the model you give it under the configured assumptions; it does not automatically prove that your TypeScript implementation matches that model. Use model-checking counterexamples to improve your design, then encode the same requirements in integration or property-based tests that exercise the implementation.
For a small number of mathematically demanding algorithms, a proof assistant such as Lean may be appropriate. It is a much larger investment than adding a unit test. Reserve it for algorithms or invariants whose correctness is unusually important and for which the team is prepared to maintain a formal specification and proof.
5. Keep agent instructions short, specific, and subordinate to code
Once the codebase and verification tools carry most of the rules, written instructions can become shorter and more useful. Put a concise AGENTS.md (or the instruction file your coding agent reads) at the repository root. Include:
- The architecture map: which directories own domain logic, UI, infrastructure, and runtime-specific code.
- The required commands: type checking, linting, dependency validation, unit tests, and the relevant end-to-end tests.
- The definition of done: acceptance criteria, expected error handling, migration requirements, and which verification artifacts to attach.
- The approved patterns: links to real examples in the repository rather than a long catalogue of abstract rules.
Avoid turning every past correction into a permanent paragraph. Agents can overgeneralize one-off advice, and large instruction files become difficult to keep accurate. If an instruction can be checked by the compiler, linter, dependency analyzer, or test suite, move it there. Keep prose for intent and judgment that cannot reasonably be encoded.
6. Make verification part of every pull request
A tool only creates trust when it runs consistently. Add a single verification command and wire its component checks into your CI system. For example:
{
  "scripts": {
    "typecheck": "tsc --noEmit",
    "lint": "eslint .",
    "check:deps": "depcruise --validate .dependency-cruiser.cjs src",
    "test:unit": "vitest run",
    "test:e2e": "playwright test",
    "verify": "npm run typecheck && npm run lint && npm run check:deps && npm run test:unit"
  }
}
The exact commands vary by project. A monorepo may need to run these per workspace, and end-to-end tests may run in a separate CI job with a test database and browser dependencies. The important point is that the agent and the CI server run the same checks. Do not rely on an agent’s statement that it ran a command; use the CI result as the independent gate.
For browser-visible changes, require a targeted end-to-end test and a screenshot or trace when it adds useful evidence. For changes to a domain rule, require tests that express the invariant. For architectural changes, require the dependency check. A change should produce evidence that matches the risk—not the same generic test checklist every time.
7. A practical adoption plan for an existing TypeScript project
You do not need to rebuild the repository before agents can help. Introduce the trust layers incrementally. A practical order is:
- Start with the last ten painful pull requests. List the repeated corrections: unsafe imports, unhandled promises, duplicated business logic, missing validation, or UI regressions. Choose the three most common and most expensive patterns first.
- Establish a baseline. Add a strict type-check command and ESLint. If the repository has a large backlog, make new violations fail first and track existing debt separately. Do not hide every finding with broad ignore patterns.
- Enforce one or two architecture rules. Add dependency-cruiser rules for the most important boundaries, such as client versus server or domain versus infrastructure. Fix violations where practical and document any narrow exceptions.
- Protect critical behavior. Add unit and integration tests around the business rules agents change most often. Use fast-check when the behavior has clear properties over a wide range of inputs.
- Add runtime verification. Set up Playwright for the handful of user journeys where a broken UI would be costly. Capture traces on failure and maintain a feature map.
- Improve agent instructions last. Keep the repository guide short and point to the commands and examples that already exist. Every recurring correction should prompt the question: can the system enforce this instead?
Track whether the investment is working. Useful measures include escaped defects, reverted changes as a percentage of merged changes, flaky-test rates, time spent reworking agent output, CI failure categories, and application performance. Pull-request volume alone is not a quality metric. The speaker’s team used its own release and revert data to assess progress; your project should establish its own baseline and improve against it.
8. Do not automate merging before you have trustworthy gates
The final layer is the outer automation loop: agents can pick up issues, implement changes, run tests, open pull requests, and in carefully selected cases merge changes automatically. But that should be the result of the trust work—not the starting point.
Before enabling auto-merge, make sure branch protection requires the relevant CI checks, permissions are scoped, secrets are not exposed to untrusted workflows, deployment and rollback are understood, and someone can audit what the automation changed. Begin with low-risk changes and keep human approval for security-sensitive, data-destructive, permission-related, or high-impact migrations. A passing test suite is evidence, not proof that every possible failure has been ruled out.
A useful progression is: agent proposes a change; CI verifies it; a human reviews the evidence; then, after the process has demonstrated reliability, expand automation to narrowly defined change types. Add broader fuzzing or exploratory browser runs when the foundations are strong enough to make their findings actionable.
Final checklist
- The TypeScript compiler runs in CI with strict checks appropriate to the project.
- Runtime inputs are validated before they are treated as domain types.
- Typed ESLint rules catch recurring mistakes, including unhandled promises and unsafe values.
- Dependency rules prevent forbidden architectural imports and circular dependencies.
- Important business invariants are covered by unit, integration, or property-based tests.
- Critical user journeys are exercised in a real browser, with useful traces or screenshots available on failure.
- The agent has a short feature map, approved patterns, and one dependable verification command.
- Automation is introduced gradually, with protected branches, limited permissions, and a rollback path.
Conclusion: trust is an engineering property
The most important lesson from the talk is not that agents should be allowed to write more code or that humans should stop reviewing pull requests. It is that the environment should make correct changes easier to produce and incorrect changes easier to detect. Clean architecture, strict types, lint rules, dependency constraints, and meaningful verification reduce the number of decisions that must be re-litigated in every review.
Start by making your TypeScript codebase a better source of examples. Turn repeated corrections into deterministic checks. Give agents a real way to run the application and produce evidence. Add formal methods only where the problem justifies them. Then—and only then—expand the amount of work your agents can do without direct supervision.
That is how you turn higher code-generation throughput into higher-quality software delivery: not by trusting the model more, but by engineering a system that deserves your trust.